This is to introduce a new nProbe feature that brings IPS (Intrusion Prevention System) support via nDPI for Linux and FreeBSD (including OPNsense and pfSense). As shown in the picture below, nProbe…
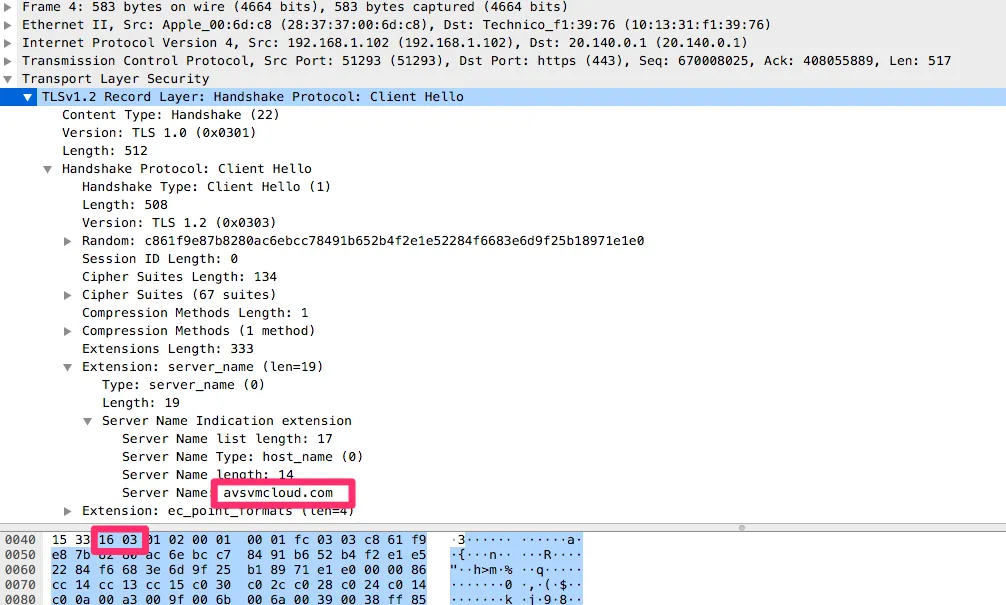
At the upcoming Sharkfest Europe 2021 we’ll talk about using Wireshark in cybersecurity. Part of the talk will focus on nDPI and Wireshark integration. Since the last release nDPI features flow risk…
In this post Martin shows how he has used ntopng to detect Qakbot trojan. Many thanks for this contribution. Introduction I am using ntopng for network monitoring quite some time now and…
Most people use nProbe and ntopng to collect flows using an architecture similar to the one below where nprobe and ntopng are started as follows: nprobe -3 -i none -n…
Telemetry protocols such as sFlow/NetFlow, SNMP or packet-based traffic analysis are the source of data for network traffic monitoring. For a long time visibility was the main issue and people were attracted…
Due to pandemic, many people are now working in a delocalised world: some work from home, others from the office. To make things even more complicated, in the past remote workers used…
We are proud to announce that a couple of talks have been accepted at FOSDEM 2021, one of the most important FOSS conferences in the world that this yar will take place…
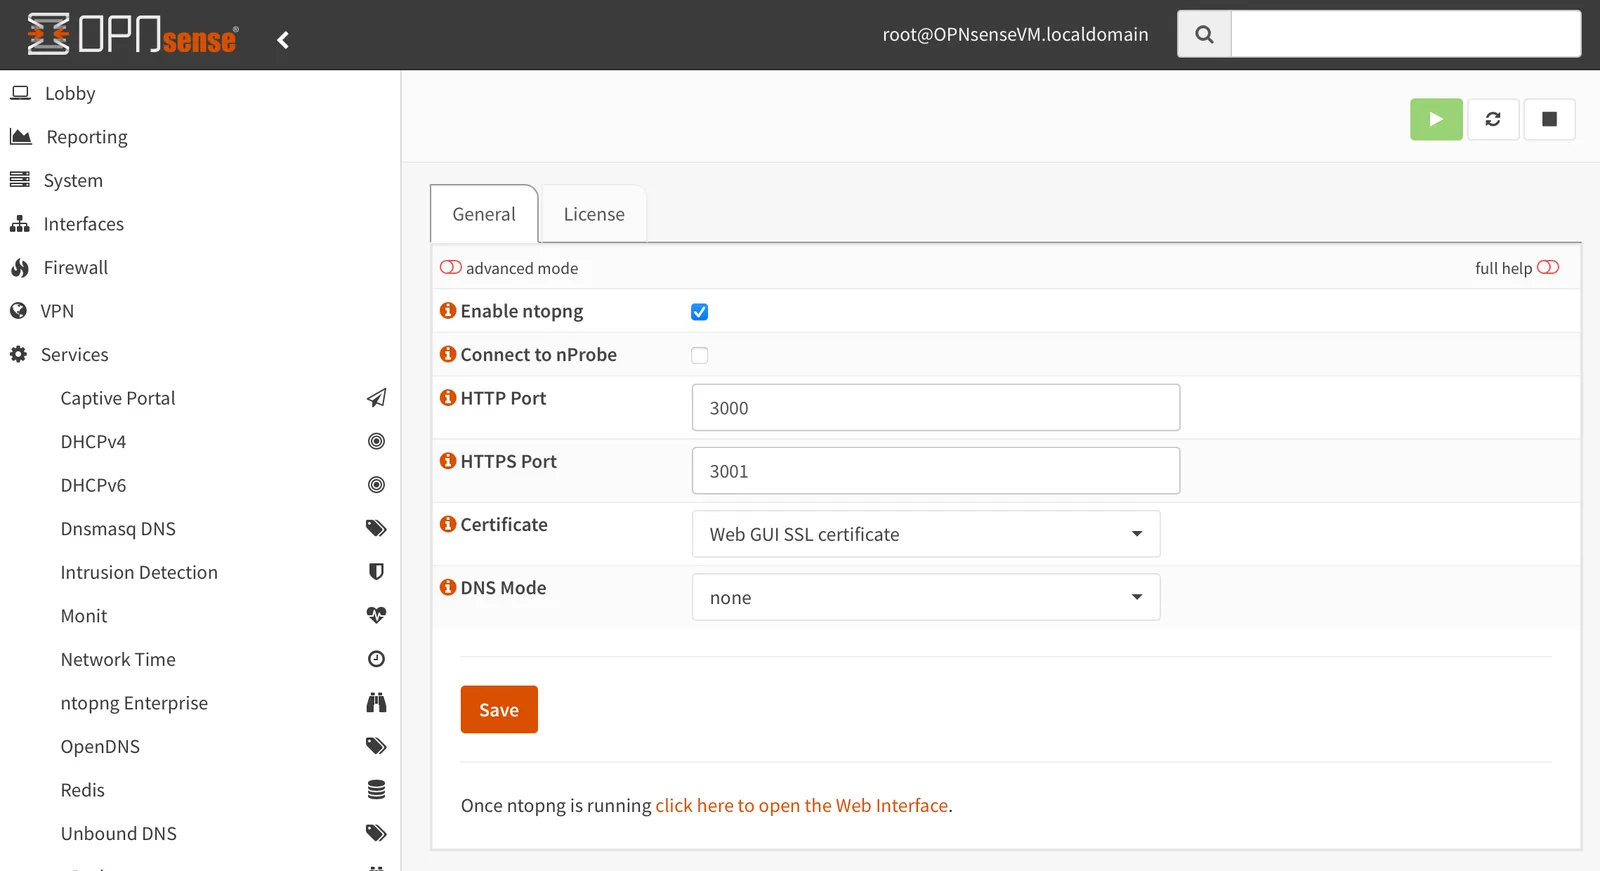
This is to announce the immediate availability of both ntopng and nProbe for OPNsense, pfSense and FreeBSD, directly supported by ntop, with nightly builds and all the features present on all other…
This is to announce nProbe 9.4 stable that is an incremental update of 9.2 released last fall. The goal of this maintenance release is to pave the way to pervasive embedded systems…
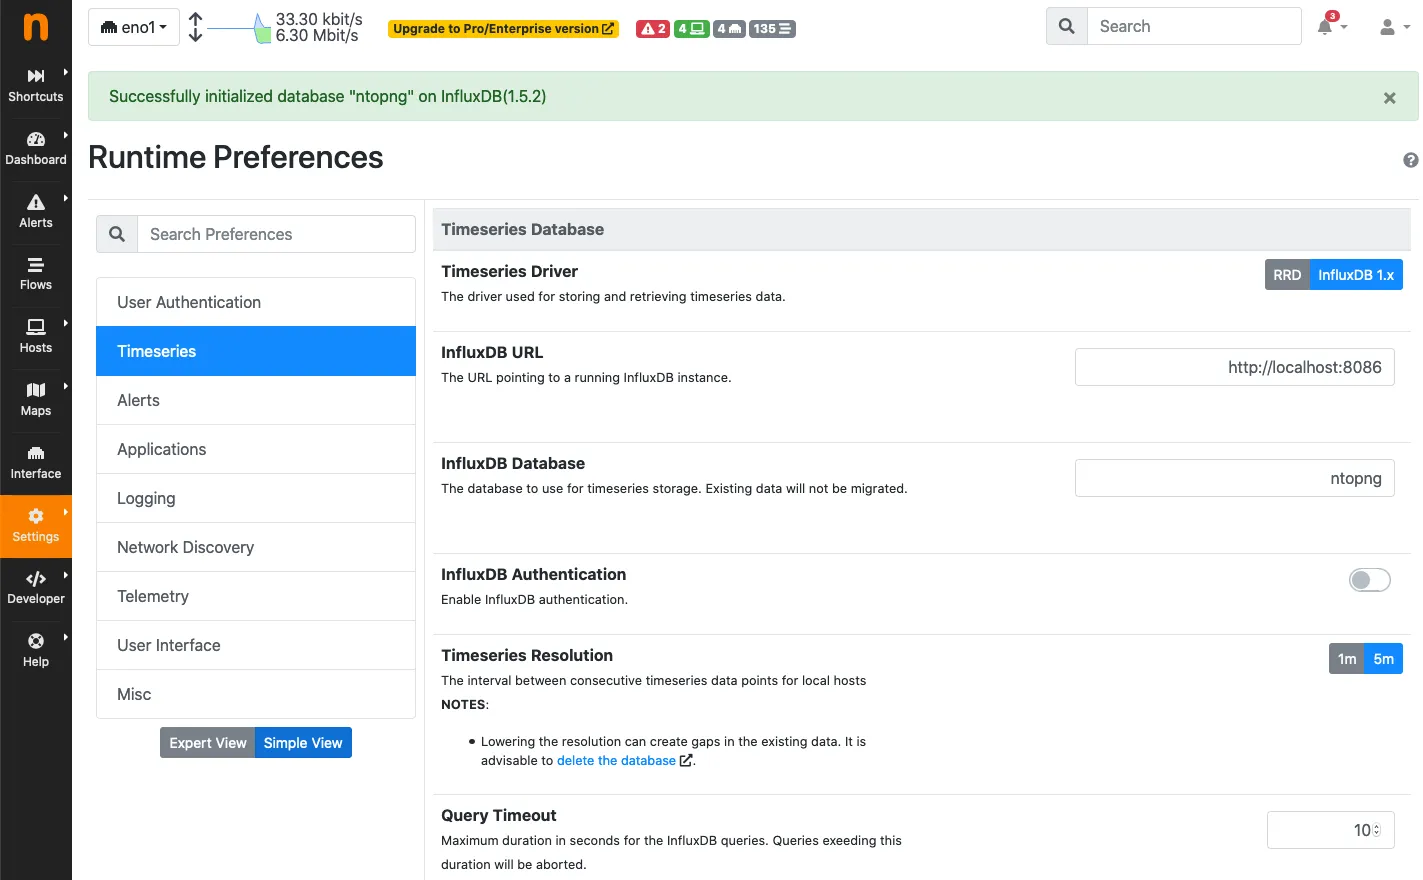
Creating Grafana dashboards out of ntopng data basically boils down to: Configuring ntopng to export timeseries data to InfluxDB Configuring the Grafana InfluxDB datasource to extract timeseries data from InfluxDB Adding Grafana…
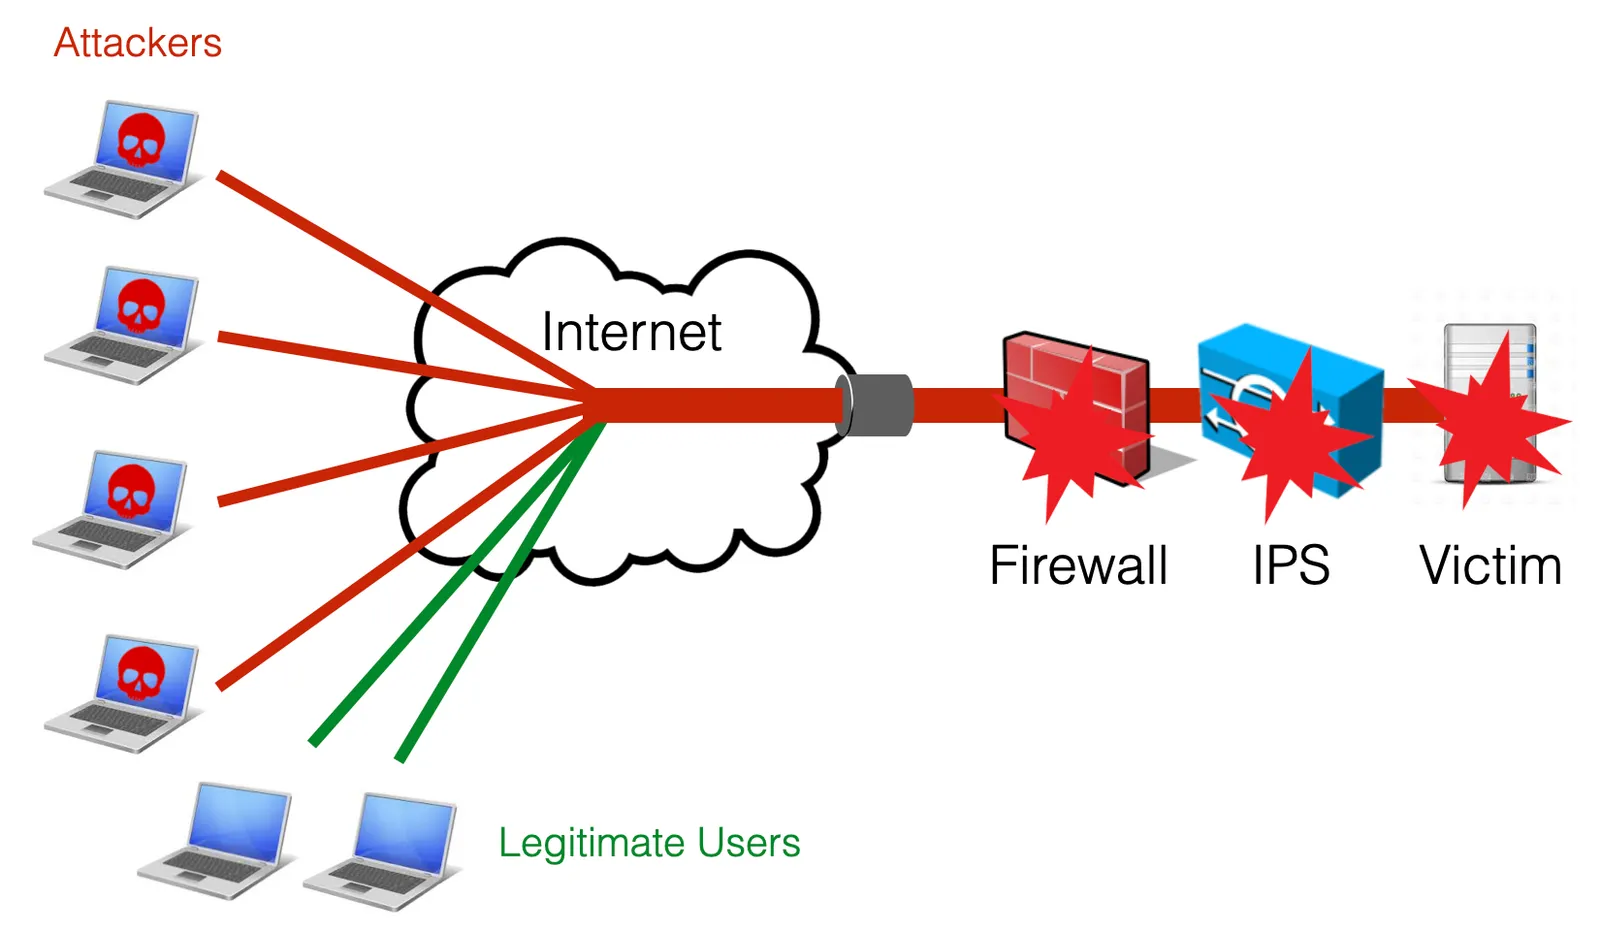
Distributed Denial of Service (DDoS) attacks represent a family cyber-attacks that are more and more common nowadays. They aim to make the service unavailable by overwhelming the victim with high traffic volumes…
Earlier this month a new highly evasive malware attacker named SunBurst has been disclosed. Immediately some countermeasures have been disclosed and in particular some Snort/Suricata rules have been published. We have analysed…