For years traffic monitoring tools assumed traffic was in clear text. This because when the Internet was created all the main protocols such as DNS, HTTP, SMTP, Telnet, POP were in clear.…
RFC8520 (Manufacturer Usage Description) specifies what is the intended (from the manufacturer standpoint) network behaviour of a network device. Being it defined in JSON format by the device manufacturer, it can be…
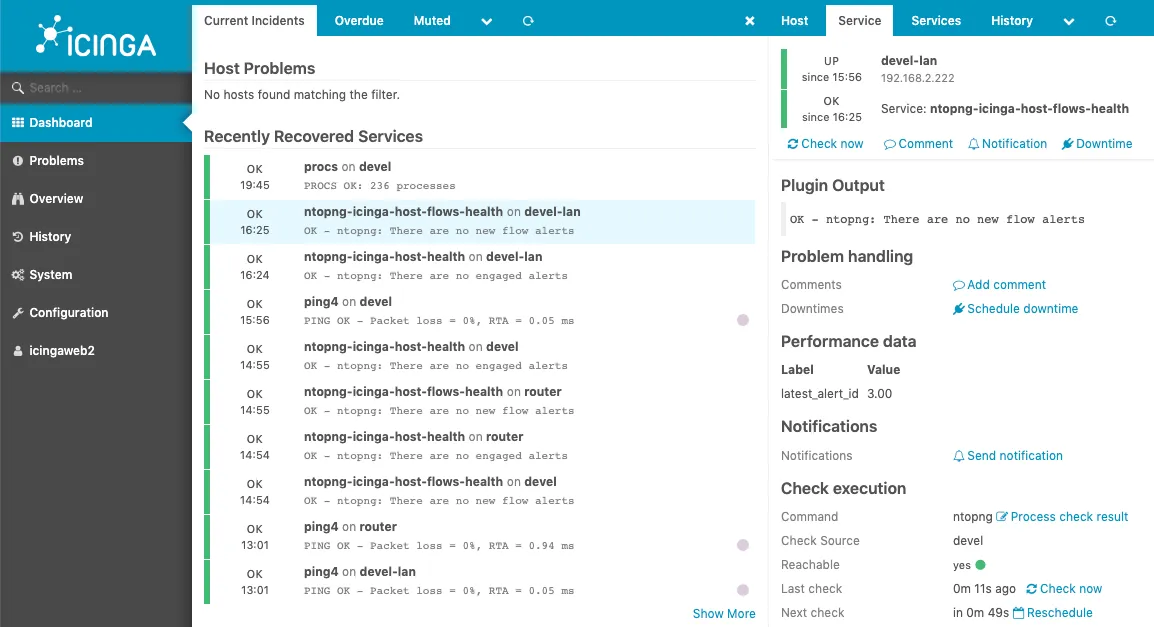
Icinga2 is an open source monitoring system which checks the availability of hosts and services, notifies users of outages and generates performance data for reporting. Thanks to its scalability and extensibility, it…
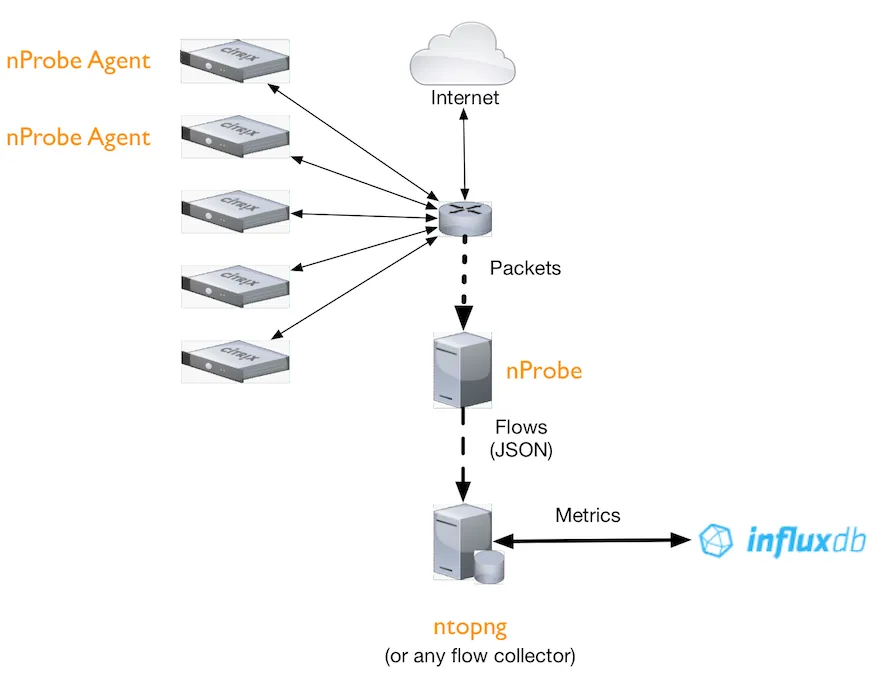
nProbe (and ntopng) is a traditional packet-based application, whose lifecycle is Capture a packet and dissect/decode it Update the representation in memory of the network traffic (e.g. the flow table) Export the…
A few months ago, with ntopng 3.8, we introduced support for continuous traffic recording, that allows you to drill down historical data from the timeseries level up to raw packets. This is…
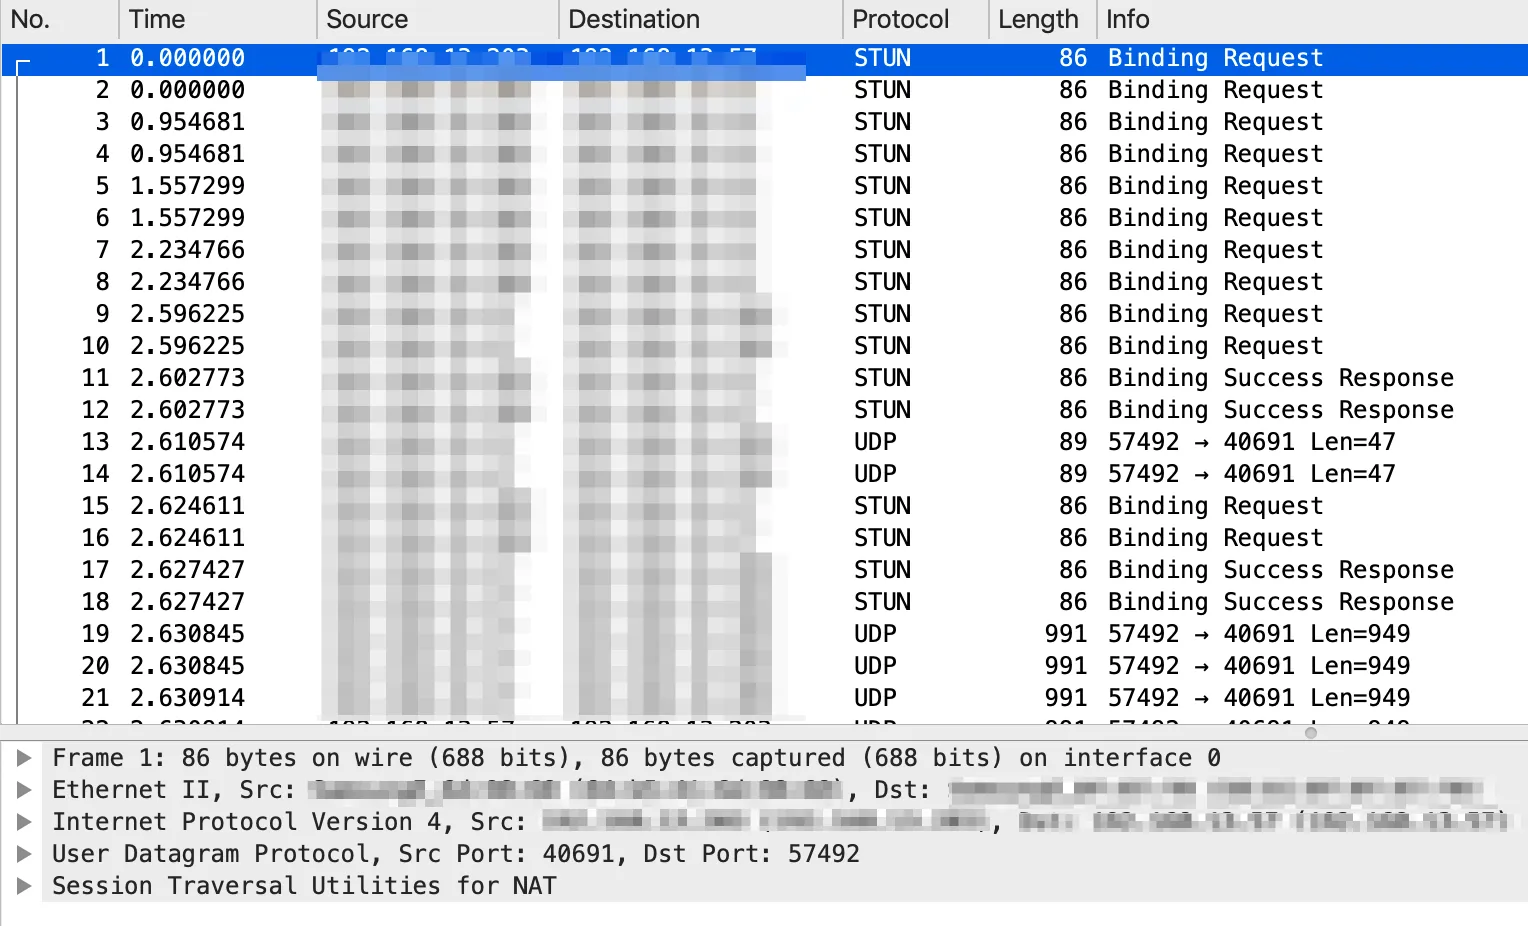
In the early Internet days, each network protocol was designed for a specific purpose: SMTP for sending emails, HTTP for the web and so on. In order to make sure that implementations…
For a while we have investigated how to combine system and network monitoring in a simple and effective way. In 2014 we have done a few experiments with Sysdig, and recently thanks…
nProbe (via its export plugin) supports ElasticSearch flows export. Setting up nProbe for the ElasticSearch export is a breeze, it just boils down to specifying option –elastic. For example, to export NetFlow…
Continuous packet recorders are devices that capture raw traffic to disk, providing a window into network history, that allows you to go back in time when a network event occurs, and analyse…
Getting started with PF_RING can be a bit tricky as it requires the creation of a few configuration files in order to setup the service, especially when ZC drivers need to be…
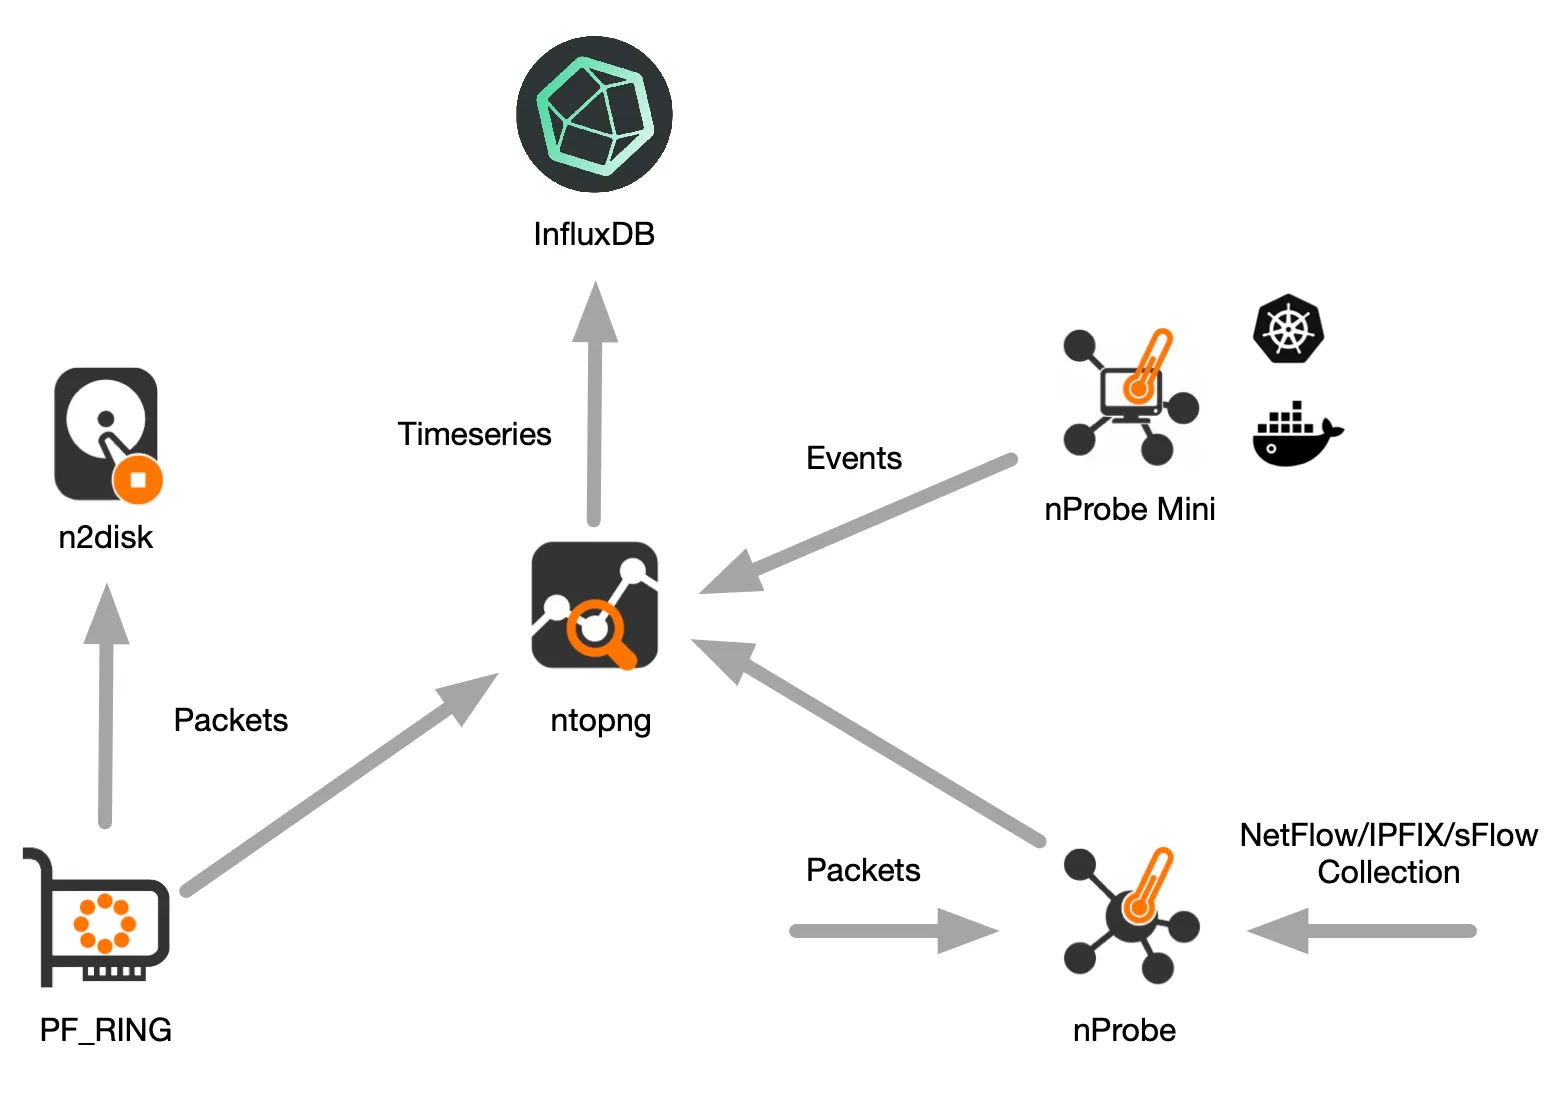
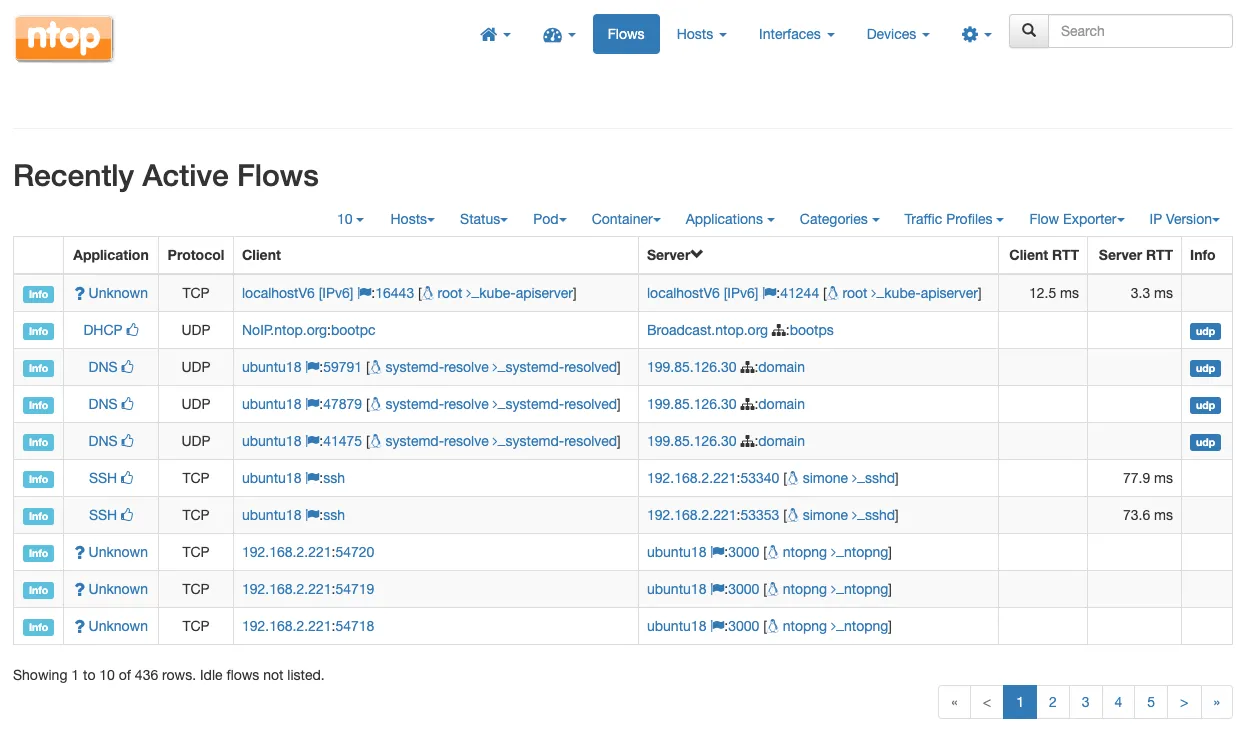
Recently, we have introduced the concept of network and container visibility through system introspection and also demonstrated its feasibility with an opensource library libebpfflow. In other words, by leveraging certain functionalities of…
A few months ago at FOSDEM we introduced the concept of network and container visibility through system introspection and we released an opensource library based on eBPF that can be used for…