Introducing PF_RING 7.0 with Hardware Flow Offload
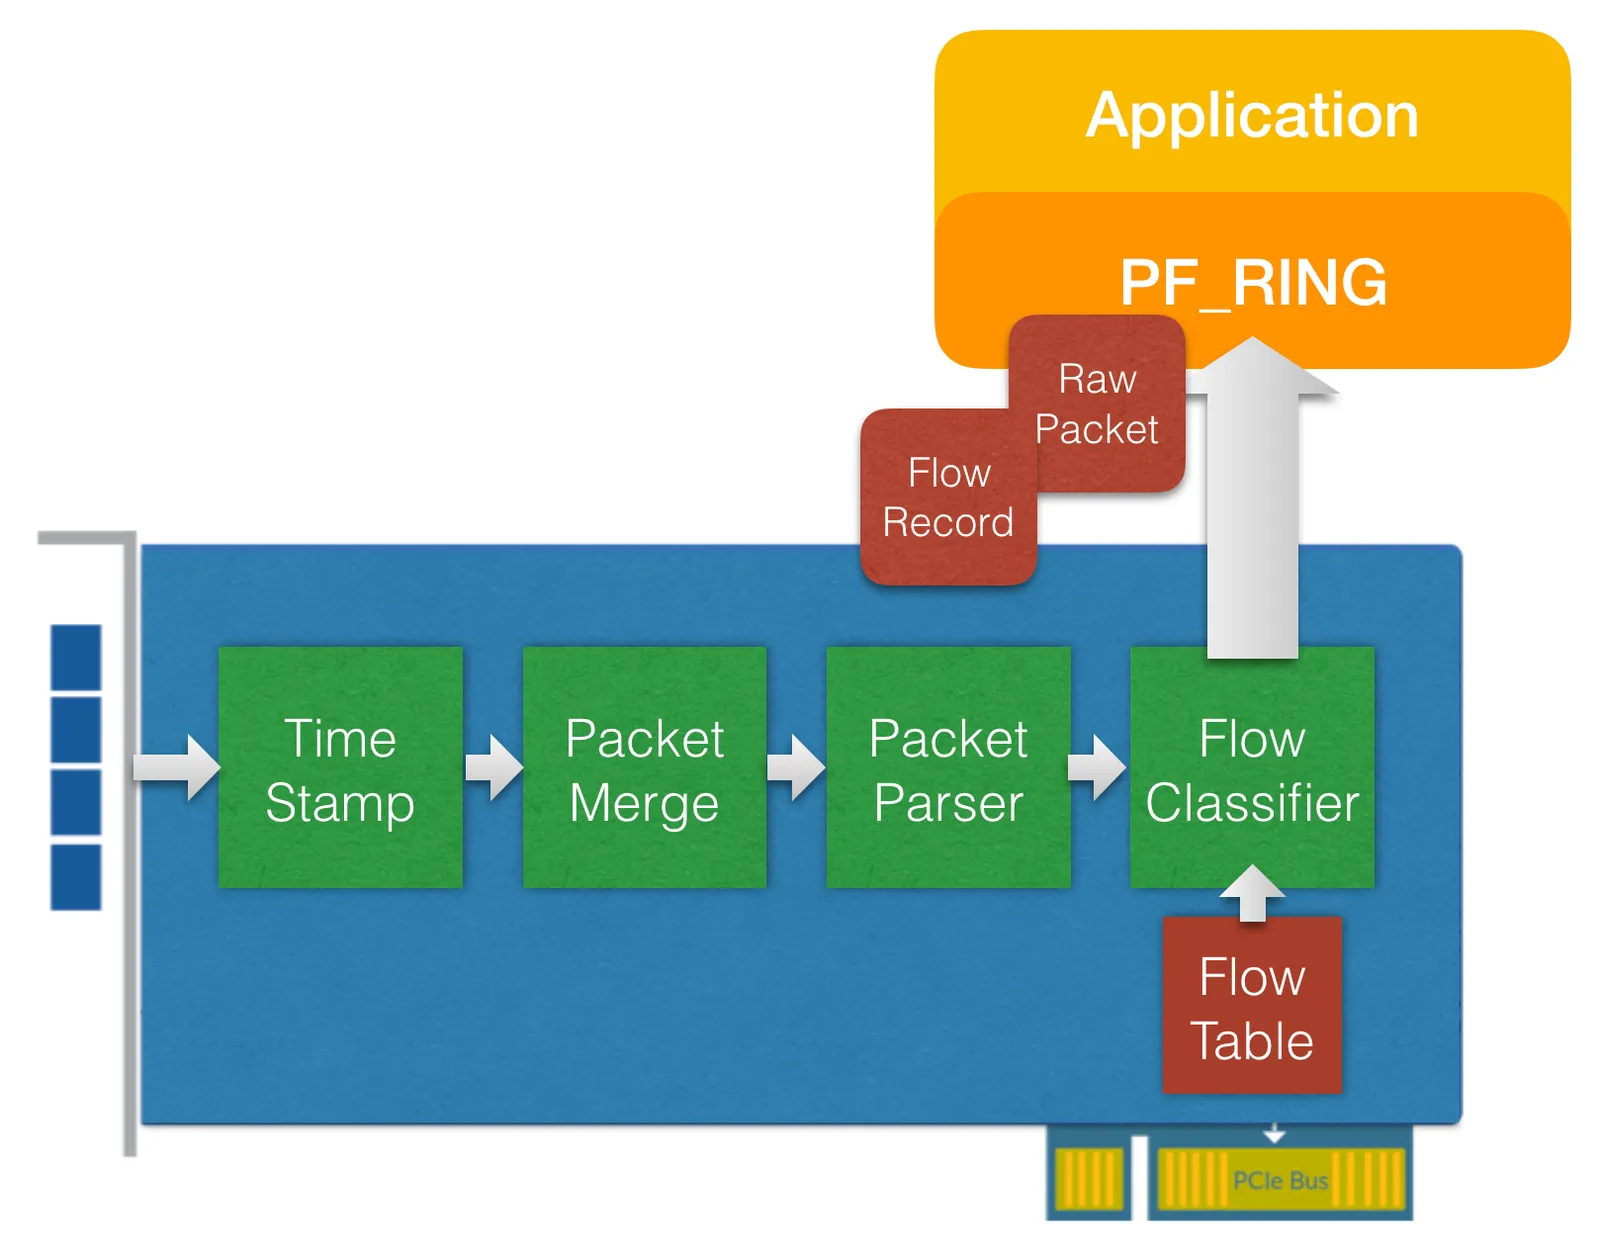
This is to announce a new PF_RING major release 7.0. In addition to many improvements to the capture modules, drivers upgrades, containers isolation, the main change of this release is the ability…
708 articles
Those who have not been able to attend our ntop meeting at Sharkfest Europe 2017 can find our presentation slides below Sharkfest EU 2017 – Intro Sharkfest EU 2017 – hardware-flow-offload Sharkfest…
Since its introduction in 1998, ntop(ng) has been a pure (well beside DNS address resolution if enabled) passive network monitoring tool. Recently we have complemented it with active device discovery in order…
This is to announce a new PF_RING major release 7.0. In addition to many improvements to the capture modules, drivers upgrades, containers isolation, the main change of this release is the ability…
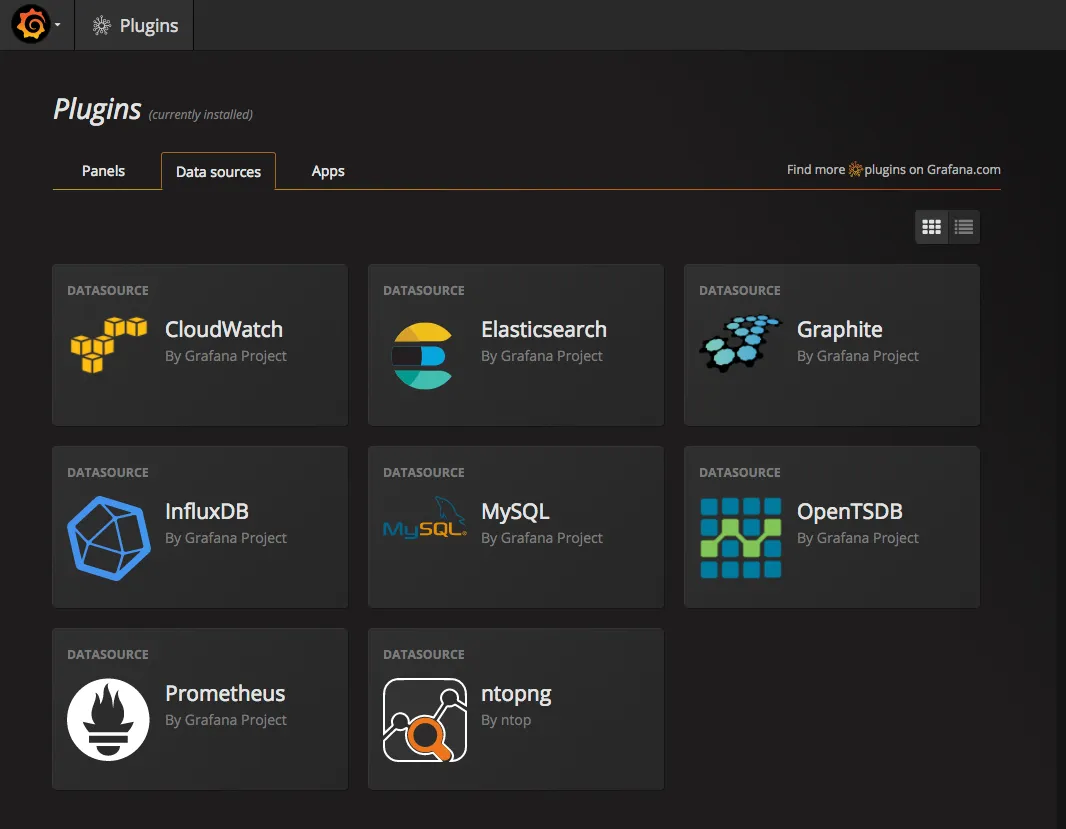
Disclaimer This article is outdated: please see this document for using ntopng with grafana Summary Grafana is one of the most widely known platforms for metrics monitoring (and alerting); ntopng version 3.1…
On November 7th we will be organising the ntop meetup during the Sharkfest EU 2017 that will take place in Portugal. You can find all details here. This year we will be…
Disclaimer This article is outdated: please see this document for using ntopng with grafana This is to announce the release of the ntopng Grafana datasource that you can find on the grafana…
This month it’s 20 years that I have started the ntop project. Initially it was a hobby project, willing to understand what was really flowing on a network after having spent 5…
Using nProbe in combination with ntopng is a common practice. The benefits of this combination are manyfold and include: A complete decoupling of monitoring activities (taking place on the nProbe) from visualization…
In early August, Scott Schweitzer interviewed me about network monitoring and packet capture. The conversation has been very broad, and I have covered various topics ranging from packet capture, network traffic analysis,…
Fritz!Box routers are popular devices that many people use to connect to the Internet. Inside these routers there is a hidden (i.e. not accessible from the router web admin page, but that…
At ntop we use wireshark to dissect traffic and to learn how to make our tools better. We’re not typical packet-oriented users however, as we want to see traffic as a whole…
This week at Sharkfest US 17, we have presented the ntop contributions to wireshark. In particular: How to use nDPI to complement Wireshark traffic classification How to remote capture on a remote…